Prompts and skills
The instructions that shape how an agent interprets a task and decides what to do.
Don't just see what agents do. Stop the wrong action before it runs.
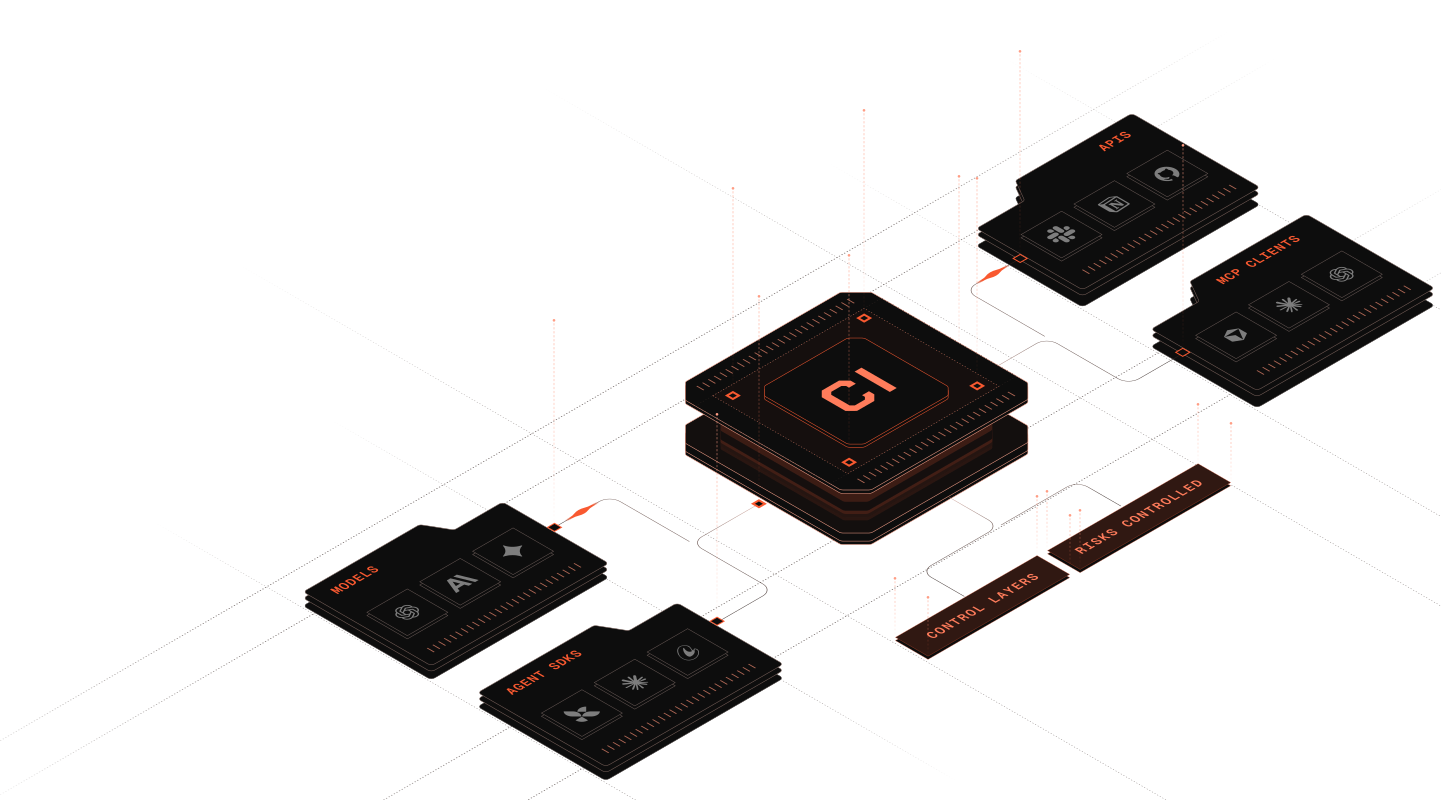
See every agent running on the endpoint. Control what each one can access, call, and reach.
The instructions that shape how an agent interprets a task and decides what to do.
The retained and retrieved information an agent uses to make decisions.
The services and actions available to an agent at runtime.
The credentials, sensitive data, and systems exposed when an agent acts.
A lightweight CodeIntegrity sensor discovers the AI agents running across your environment, maps the tools and data within their reach, and enforces policy before unsafe actions execute.
CodeIntegrity showed us the highest-risk path in our agent environment, from the identity behind the agent to the data and tools it could reach. We knew exactly where to act first.
Give teams the agents they want while security governs the data, tools, and systems each one can reach.
Detect and block unsafe actions at runtime, before sensitive data leaves or high-impact changes execute.
Connect agent intent, policy decisions, and outcomes so security can explain what happened and prove control.
What it covers, how it protects, and where it fits.
Yes. CodeIntegrity helps you find and assess the MCP servers, tools, and skills connected to supported agents, including unapproved ones.
Yes. CodeIntegrity can stop unsafe agent actions before they reach your tools, data, or systems.
No. It combines visibility with active controls that can prevent unsafe actions before they run.
CodeIntegrity addresses prompt injection, data leakage, intent drift, memory poisoning, excessive agency, and risky MCP or skill configurations.
CodeIntegrity is designed to protect supported agents and connected tools without requiring teams to rebuild their existing workflows.
Yes. CodeIntegrity can be self-hosted so agent activity and sensitive data remain within your security boundary.
Security teams gain visibility and control, while developers keep using the agents and tools that help them work.
Run CodeIntegrity inside your security boundary so agent activity, sensitive data, and enforcement stay within your environment.